Credentials
Certified Information Security Manager (ISACA). M.S., University of North Texas. SANS Cloud Security and DevOps Automation, July 2019 (38 CPE).
Hello, I'm
I secure critical infrastructure leveraging my 10+ years of expertise.
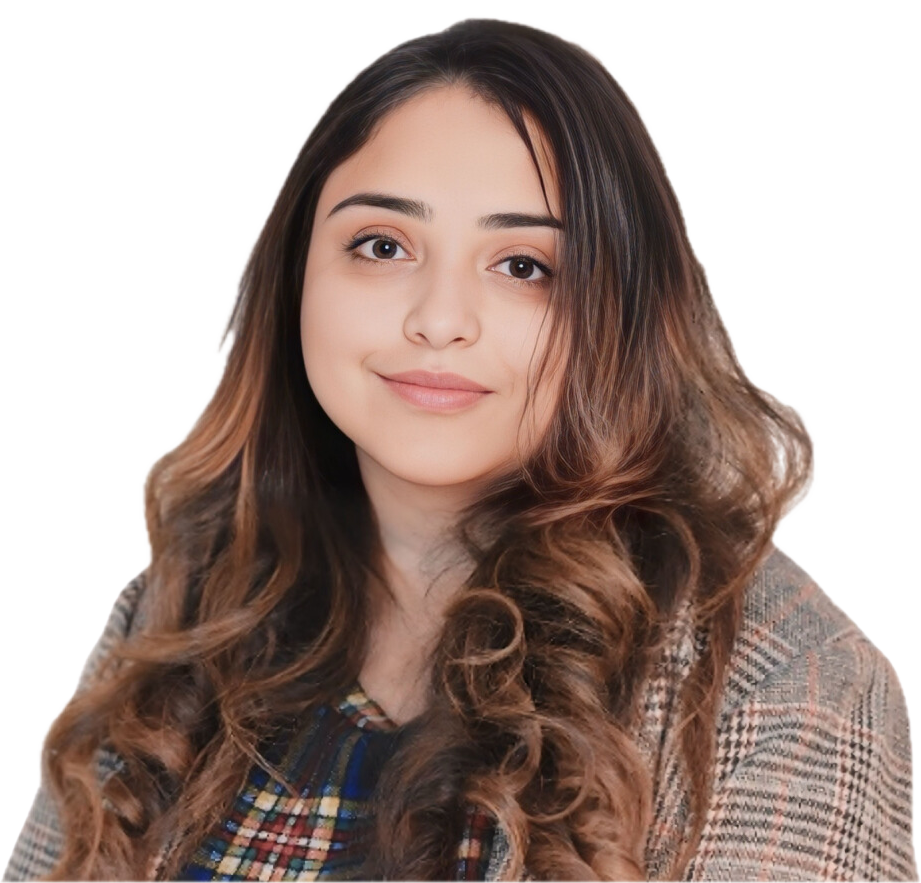
Critical infrastructure needs security that is designed with meticulous care and precision.
I'm a cyber security product specialist at World Wide Technology. I hold an M.S. from the University of North Texas and the CISM certification from ISACA.
My research looks at the systems that keep power and fuel flowing: NERC CIP and NIST compliance, malware in operational technology, ransomware resilience for SCADA, and identity and access management. In 2025 I received the Gold Award for Cybersecurity Architect of the Year at the Cybersecurity Excellence Awards.
Certified Information Security Manager (ISACA). M.S., University of North Texas. SANS Cloud Security and DevOps Automation, July 2019 (38 CPE).
Single sign-on and identity and access support for a NERC CIP BCSI repository serving more than 40,000 users, with security controls across AWS, Azure and GCP aligned to SOC 2, NERC and NIST.
Section Editor, ESP Journal. Invited keynote at ICICCS 2024 (as noted in the ICI3T 2026 reference letter).
Roles have included PG&E, RingCentral, Deloitte & Touche, Assurant Insurance and T.S. Web Technology (per Outlook India), and Graduate Teaching Assistant at UNT College of Business. Currently at World Wide Technology.
Led a cyber asset visibility initiative across 800,000+ assets at a U.S. utility serving 16 million+ customers, replacing manual inventory reconciliation with correlation logic that explains why assets drop out of governance. Featured in The Hacker News, September 2026.
Full-time cybersecurity and program management role.
Runs the operation, configuration, monitoring and reporting of security products. Leads incident response and root cause analysis, recommends control and tooling upgrades, and builds automation with compliance teams and vendors.
Kept a 24/7 production environment available through root cause analysis, automated testing and deployment, proactive monitoring and self-healing systems, and on-call incident response.
Integrated security into DevSecOps pipelines and secrets management, ran gap analysis and remediation for SOC 1 and SOC 2 audits, and supported SOX, HIPAA, HITRUST, FedRAMP and GDPR compliance. Automated AWS policy-drift checks in Python and secured containers with Twistlock and Aqua.
Automated Behat and Selenium testing, introduced CI/CD with Jenkins, Bamboo and CircleCI, and connected hosting on Pantheon and AWS with Jira and Slack.
Designed IT general controls for a cloud-native environment and drafted the SOC 2 and HITRUST framework for platform-level controls. Led the infrastructure audit across 100+ servers and 200+ databases for a major financial and insurance client, with teams in more than 10 countries.
Supported lectures and coursework and mentored students one to one.
Built CI/CD pipelines with Jenkins and Bamboo, deployed and monitored AWS infrastructure with Puppet, and delivered Salesforce projects across the full development life cycle.
Peer-reviewed work on critical infrastructure security, and an industry award.
 Award, 2025
Cybersecurity Excellence Awards
 Google Scholar
As of October 2026
 Journal
Two 2021 papers: NERC CIP and NIST compliance, and malware detection in operational technology.
Press, October 2025An AI app for tracking and protecting wildlife.
[pending: confirm the ICICCS 2024 keynote and any others]
ComSIA 2026, Springer Lecture Notes in Networks and Systems (accepted proceedings), with U. Chakrobortty Best Paper
The paper looks at how to protect the sensors that oil and gas operations depend on from cyberattacks. It brings AI-based threat detection down to the sensor hardware itself, which has tight power and computing limits.
ICCCNet 2025, Springer LNNS vol. 1856, pp. 434–446, sole author Best Paper DOI 10.1007/978-3-032-18913-4_41
The paper compares four established risk-management models for critical infrastructure with a new model the author proposes. It tests all five on spotting, assessing and reducing risk. In the award letter's account, the new model did better on each stage and held up as the amount of input grew.
Journal of Computational Analysis and Applications, vol. 31, no. 1 (Eudoxus Press, article 4323) [pending: exact title and link]
This paper argues that automation is now essential for monitoring Bulk Electric System Cyber System Information (BCSI), the sensitive configuration, network and log data that keeps power grids running.
IEEE SMART-2025, with A. Gogineni Best Paper DOI 10.1109/SMART66937.2025.11389477
The paper proposes a way to manage who can access what across cloud and on-premises systems without gathering sensitive identity data in one place. It combines federated learning with privacy protections, and it considers attacks such as poisoned models and data inference.
SoutheastCon 2026, with V. Kumar and G. C. Kakaraparthi
The paper discusses how ethical governance frameworks could guide advanced AI used in systems that connect software to physical equipment, such as power grids and industrial plants.
International Conference on Data Science and Big Data Analysis, 2025, with S. K. Malaraju
The paper looks at how oil and gas operators can prepare for and recover from ransomware attacks on the control systems that run their facilities.
Int. J. Multidisciplinary Research 3(4), 1–10
The paper examines how utilities can manage the risk from long-running, targeted attacks on their critical systems.
J. Adv. Dev. Res. 12(2), 1–12
The paper looks at how malware can reach industrial control equipment through suppliers and software, and at ways the oil and gas industry can reduce that risk.
ESP Journal of Engineering & Technology Advancements 1(1), 273–281
The paper compares two major security compliance frameworks, NERC CIP and NIST, and uses the comparison to define a framework for building more cyber-resilient infrastructure.
A Gold Award named me Cybersecurity Architect of the Year, and I have received three Best Paper Awards from international conferences in India and the UK. The conference proceedings are published, or slated for publication, by Springer or IEEE.
Cybersecurity Excellence Awards
View the awardUniversity of Delhi
One of no more than 24 Best Paper Awards among 280 accepted papers (about 8.6%), from about 1,900 submissions. Springer LNNS.
Manchester Metropolitan University, UK, sole author
Proposed risk model outperformed four baseline models across identification, assessment and mitigation. 422 papers shortlisted for publication in ten Springer LNNS volumes.
View the paperInformation Security & Engineering Track, IEEE Conf. Record 66937, co-author
Blind review by at least three experts; only papers rated +3 were eligible. Published on IEEE Xplore.
View the paperBeyond my own research, I have been invited to guide the work of others: delivering a keynote on securing critical energy data, speaking and chairing a session at international conferences, convening a conference, and evaluating entries on an awards judging panel. Each role draws on my hands-on experience protecting regulated utility infrastructure.
Cybersecurity and Risk Management judging panel
Appointed to evaluate submissions for technical merit, practical application and potential industry impact (announced 15 January 2025).
Read the announcementInternational Conference on Intelligent Computing, Communication, and Technology
Served as Convener, supporting planning, stakeholder coordination and the technical program.
Proceedings: Procedia Computer Science vol. 282 (Elsevier)
“Importance of Identity and Access Management in setting the BCSI-NERC repository.”
Hybrid, with University of Calabria, Italy
“Automated Security Monitoring for NERC BCSI Repositories: Building Audit-Ready and Resilient Critical Infrastructure.” Joint events drew about 3,000 submissions from 28 countries.
Invited by the organizing committee. 1,200+ submissions from 18 countries, 180 accepted (15%), 300 participants.
My “Lost and Found Animal Tag” is a German utility model, registered with the German Patent and Trade Mark Office (DPMA) as DE 20 2025 102 267 U1. It is designed to help track and recover lost or displaced animals. I developed it alongside my AI wildlife app, Glo-Paw, to support wildlife protection.
Designed to help track and recover lost or displaced animals, and a companion to my Glo-Paw wildlife app. Outlook India (October 2025) describes it as a “Lost and Found Animal Tag”. Publicly verifiable in the DPMA register.
View the record on Google PatentsMy work on cyber asset visibility in the power grid is the subject of a contributed feature in The Hacker News. Outlook India and the Times of India covered Glo-Paw, my AI wildlife app, and its companion animal tag. My appointment to a Global Recognition Awards judging panel was announced in the press release below.
Expert Insights
“The Invisible Cybersecurity Challenge Transforming Advanced Power Grids.” Profiles her enterprise asset visibility work across 800,000+ cyber assets and the “muted asset” concept.
Read the articleHub4Business
“Suchismita Chatterjee’s Glo-Paw App Brings Technology And Community Together To Protect Wildlife.” Covers the AI wildlife app and her German-approved Lost and Found Animal Tag.
Read the articleTimes of India, Entertainment / Events
Coverage of Glo-Paw and its patent filing.
Read the articleMarketersMEDIA newswire
Announces her appointment to the 2025 Global Recognition Awards judging panel for cybersecurity and risk management.
Read the releaseConfirmations issued by conference organizers, each based on official records.
Confirms the Best Paper Award and its selectivity.
Confirms the Best Paper Award and her recognition as co-author.
Confirms the sole-author Best Paper Award.
Confirms her invited keynote, 20 December 2025.
Confirms her selection as an invited speaker.
Reference letter on her service as Convener.